NCSC warns AI-powered ransomware likely to hit UK infrastructure by 2028
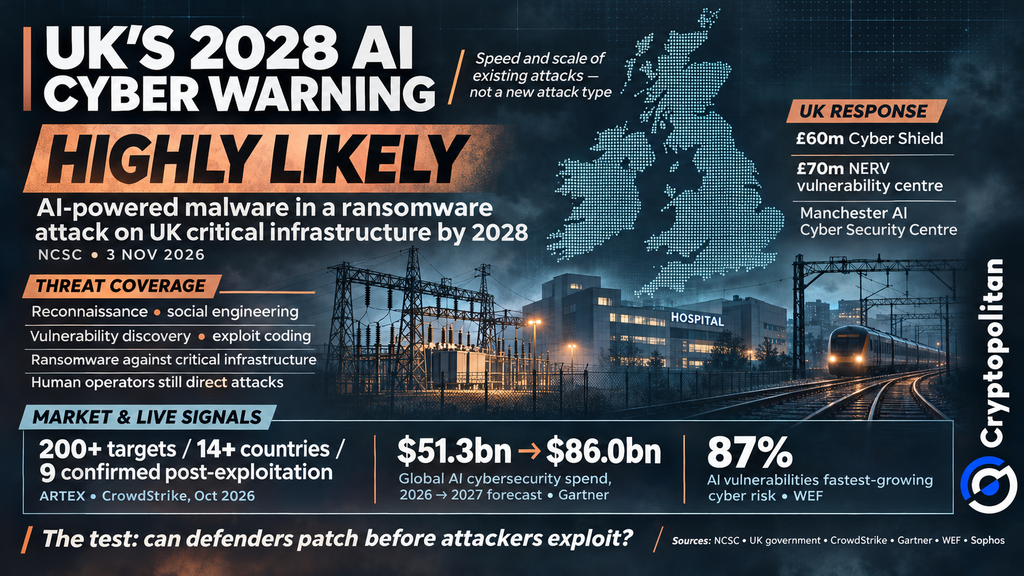
Britain’s cyber agency has warned that AI may soon help criminals disrupt essential services. On November 3, the National Cyber Security Centre (NCSC) said AI-based malware could be used in ransomware attacks against UK critical infrastructure by 2028.
The warning has not been confirmed yet. The warning covers how quickly criminals could take advantage of vulnerabilities that were tough for operators to fix.
Why the danger is speed, not a new kind of attack
AI is helping hackers carry out familiar attacks faster. The NCSC describes it as a force multiplier. It allows attackers to identify targets, create phishing messages, uncover vulnerabilities, and develop exploits more quickly. But humans still guide these operations. The International AI Safety Report confirms that no fully autonomous cyberattack, carried out from start to finish without human involvement, has been documented.
NCSC chief Richard Horne pointed to years of neglected security:
“Vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale that was once unimaginable.”
Britain has committed £60 million to a Cyber Shield and £70 million to the NERV vulnerability-scanning centre. A new AI Cyber Security Centre of Excellence is planned for Manchester. The NCSC also considers China particularly well positioned to target strategic infrastructure with AI.
AI-assisted intrusions are already documented
There are already signs of what faster attacks look like. In October, CrowdStrike documented China-linked Vapor Panda using ARTEX against more than 200 organisations across at least 14 countries. But it confirmed post-exploitation at only nine. Being targeted does not mean being breached, as Cryptopolitan reported.
Ransomware groups are also turning to AI to carry out attacks. Sophos found that Aur0ra operators used Cursor and other AI models to gain deeper access to compromised networks. The attackers provided stolen credentials and identified their targets. AI then helped them explore the networks and gain administrator privileges with little human supervision.
The results indicate the ability of AI to improve current hacking methods. This conclusion was also made by Red Canary, which states that attackers are able to hack systems more quickly in known ways using AI instead of developing new methods. According to CrowdStrike’s 2026 threat report, the problem is getting worse as the number of attacks carried out by hackers made possible by AI increased by 89% in 2025.
Who sells the shovels when everyone starts digging
The growing threat comes as companies prepare to spend more on AI cybersecurity. Gartner forecasts global spending of $51.3 billion in 2026, rising to $86 billion in 2027. Our calculations show that AI cybersecurity accounts for just 1.9% of total projected AI spending in 2026, up from 1.5% in 2025.
Cybersecurity concerns are growing worldwide. A World Economic Forum survey found that 87% of respondents saw AI-related vulnerabilities as the fastest-growing cyber risk in 2025. Another 94% expected AI to have the greatest impact on cybersecurity in the coming year. These findings show how seriously organisations view the threat, although they do not measure actual attacks. Gartner’s spending forecasts were also released before the NCSC’s November 3 warning.
Can defenders patch faster than attackers exploit
But spending more on cybersecurity does not automatically make critical infrastructure safer. Britain’s Cyber Shield and NERV centre could help organisations identify vulnerabilities sooner. Fixing them is another challenge. Operators still need money, skilled workers and time to upgrade ageing systems. The NCSC warns that older infrastructure could remain vulnerable as AI makes attacks faster and cheaper. For essential services already struggling with limited budgets, that creates a serious problem. The question now is whether they can fix vulnerabilities before attackers exploit them.
This story was originally published by Cryptopolitan. Read the original article.